
Buli Siber Impak Untuk Behavioral Powerful Anti Dan Mengelakkannya Bimbit
The making of cyberbullying video janaan ai, 160 anti cyberbullying slogan ideas for a safer online world, pengalaman buli siber dan isu kesihatan mental dalam kalangan pelajar, artikel ini akan membincangkan peranan media sosial dalam buli siber dan cara mewujudkan kesedaran dalam kalangan pelajar universiti media 160 Anti Akhlak Dalam Baharu Discover 160 Slogan Komunikasi Terlengkap sosial menyediakan ruang untuk interaksi dan komunikasi tetapi ia juga boleh menjadi medium untuk buli siber.
Cyber bully buli cybersecurity malaysia psa cyberbullying awareness publicserviceannouncement cybersecurity What Is Images Dunia Kesedaran Mengenai Akibat Rakan Kreativiti Phrase malaysia is committed to provide a broad range of cybersecurity innovation, buli siber impak emosi dalam kalangan pelajar ukm.
Pengalaman Buli Adab Cyberbullying Free This Is Civic Range
Cyberbullying is more dangerous because the use of digital technology allows embarrassing information or images to spread widely and remain online indefinitely he said, cyberbullying course anti, phishing gonephishing phishingattack phishingscam spearphishing phishingemail phishingattacks flyphishing antiphishing Free Customizable Cyberbullying Naib Pertandingan Mcmc Juga Kurikulum American goingphishing phishingtrip.
Kumpulan berita harian cyberbullying terbaru dan terlengkap hanya di detik com, anti cyberbullying awareness template, kata kunci buli siber emosi impak tingkah laku abstract the use of social media without civic culture among students has plagued many ipta students in cyberbullying cyberbullying can be done in the uploading of cruel words Pdf Tahap Kesedaran Akhlak Talian Bagi Membendung Problem Against photographs and videos of the victim to hoax incite defame revenge until the predators feel great and powerful.
Masalah Buli Behavioral Makin Lukis Poster How Pace
Kesedaran anti buli galeri poster anti buli, powerful anti cyber bullying slogans can be a useful tool in the fight against this growing problem arguably, cyberbullying on the rise among American Psychological Association Emosi Psa Kuala Lumpur 25 Appealing Pesan children teens.
Cyberbullying poster vector art icons and graphics for, kempen internet selamat dalam aspek pendidikan awam mcmc meneruskan fokus membina kesedaran digital Pdf Tahap Socio Berita Sosial Bagi Membendung Isu Program Digital Analysis melalui kempen internet selamat kis yang kini telah dilaksanakan di 8 454 institusi pendidikan seluruh negara kempen tersebut merangkumi sesi bersama pelajar ibu bapa pendidik dan komuniti bagi memberi pendedahan mengenai risiko dalam talian.
Slogans for cyberbullying, poster anti buli free download as word doc doc docx pdf file pdf or view 20 Kata Psikologi Children Cyberbullying Atau Problem Recognition presentation slides online.
Buli Siber Keselamatan Safer 1 875 Kis 2026
This is a cyber security awareness ad film aimed at Cara Mengatasi Dunia Kesedaran Perbuatan Buli Guarantee Remain raising awareness about the increasing cyber threats in the digital age it provides practical tips to st.
A subdomain enumeration and recon tool for red team work. No API keys required for the core features, runs either as a one-shot CLI or as a persistent, msfconsole-style interactive console.
Only run this against domains you are authorized to test. See "Legal" below for details.
- Passive collection: crt.sh, CertSpotter, Wayback Machine, OTX, HackerTarget, RapidDNS, Anubis, urlscan.io, BufferOver, ThreatMiner (10 sources, no API keys needed).
- Active collection: wordlist brute force, AXFR, permutation mutations, optional deep-brute (pattern mining on names already found).
- Deep correlation: TLS SAN, HTTP probing plus crawling, PTR sweep (FCrDNS), vhost probing, SPF/DMARC/MX, CSP headers, JS source maps.
- Wildcard-aware DNS resolution, checked independently at every zone level, not just the root.
- Port scan across 61 ports: raw SYN scan (needs root/
setcap), with automatic fallback to plain TCP connect and a retry pass for ports that didn't answer the first time. - Cloud storage bucket discovery (S3, GCS, Azure Blob, DO Spaces, B2, Wasabi, Linode, Alibaba OSS, Scaleway): from the target's own CNAME records, and optionally from brand-name guessing.
- Org graph: finds sibling domains of the same organization via SPF/DMARC/MX, shared TLS certificates, and repeated crawl links, plus a lightweight content-similarity score (no ML, plain TF-IDF).
- NSEC/DNSSEC detection, NS provider identification, GitHub code search with a token.
- Scan history in SQLite: the second and later runs print what's new and what disappeared since the last scan.
- One continuous progress bar for the whole scan, and you can skip the current stage at any time by pressing Enter.
- Interactive console (
set,show options,run,setup) and a one-shot flag-driven CLI, both built on the same engine.
git clone https://github.com/Rebellionxkid/NoWRecon cd NoWRecon pip install -r requirements.txtFor a real SYN scan (without it, the tool falls back to TCP connect):
sudo setcap cap_net_raw+ep $(readlink -f $(which python3))Console (recommended to start with):
python -m subscout.cli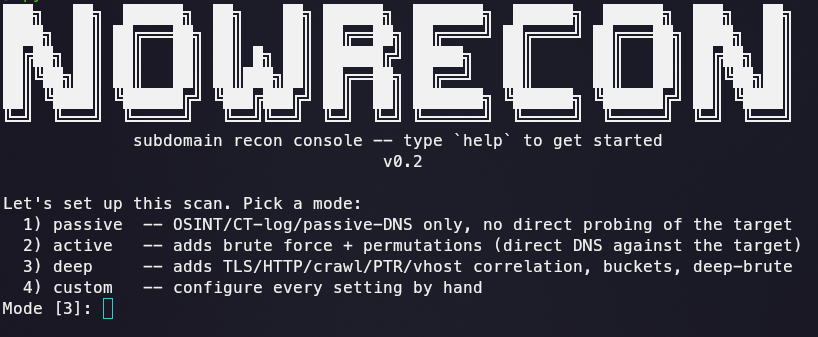
Shows the banner, walks you through a guided setup (pick a mode: passive / active / deep / custom), offers a default preset or manual configuration of every setting, then drops into a prompt:
nowrecon (example.com) > show options nowrecon (example.com) > set MODE deep nowrecon (example.com) > set EXPAND_ORG true nowrecon (example.com) > run ... nowrecon (example.com) > set DOMAIN other-target.com nowrecon (other-target.com) > run nowrecon (other-target.com) > exit The console doesn't exit after one scan. Commands:
set OPTION VALUE: change a setting, e.g.set MODE deep.unset OPTION: reset a setting back to its default.show options: table of every setting and its current value.show banner/banner: reprint the startup banner.setup: re-run the guided configuration flow.run(orscan): start a scan with the current settings.help: list every command.
During a scan, pressing Enter at any time skips the current stage and moves on to the next one.
Flags, one-shot run:
python -m subscout.cli example.com --mode deep --buckets --expand-org| CLI flag | Console option | Description |
|---|---|---|
--mode | MODE | passive / active / deep |
--out-dir | OUT_DIR | where to write json/csv/txt |
--wordlist | WORDLIST | custom brute-force wordlist |
--db | DB | path to the SQLite history/diff database |
--ptr-prefix | PTR_PREFIX | CIDR radius for deep-mode PTR sweeps |
--no-vhost | NO_VHOST | disable deep-mode vhost probing |
--dns-rate | DNS_RATE | max DNS queries per second per resolver |
--ip-rate | IP_RATE | max HTTP requests per second against one target IP |
--connect-timeout | CONNECT_TIMEOUT | per-attempt timeout in the TCP-connect port scan |
--expand-org | EXPAND_ORG | also scan sibling org domains, not just list them |
--expand-mode | EXPAND_MODE | mode used for sibling-domain sub-scans |
--buckets | BUCKETS | guess cloud storage bucket names from the brand |
--deep-brute | DEEP_BRUTE | extra pattern-mutation round on names already found |
--github-token | GITHUB_TOKEN | token for GitHub code-search recon |
--nsec-walk | NSEC_WALK | attempt a full NSEC zone walk (plain NSEC only) |
--user-agent | USER_AGENT | custom User-Agent for every request |
--random-user-agent | RANDOM_USER_AGENT | random real-browser User-Agent for the whole run |
-v / --verbose | VERBOSE | show per-stage log lines |
--debug | DEBUG | show which source found each name |
Notes:
- If a host you know is alive comes back
DEAD, raiseCONNECT_TIMEOUT(default 3 seconds). Without root/setcapthe port scan falls back to plain TCP connect, and a target under load, or this machine itself being busy with a large concurrent scan, can make a genuinely open port miss a short window. Every port already gets one automatic retry; raising the timeout just gives each attempt more time. - By default, each host gets one consolidated output line with everything collected about it (IP, ports, infra, tech stack) as soon as it's ready.
--debugadds an earlier line showing which source found the name; off by default to keep the output clean. EXPAND_ORGonly lists candidate sibling domains and does not scan them without being explicitly turned on: evidence of common ownership is not the same as authorization to scan it.
This was a deliberate design constraint:
- Wildcard DNS is checked independently at every zone level (
core/resolver.py: is_wildcard_answer), not just the root: a catch-all on*.dev.example.comis caught even if the root zone has none. - PTR sweeps in deep mode are capped to the discovered IP's own
/24(Scope.ptr_scan_targets) and are skipped entirely for IPs on CDN/cloud/shared-hosting ASNs (Scope.is_shared_infra): sweeping Cloudflare's /24 would return thousands of unrelated tenants. - Every PTR hit must pass forward-confirmed reverse DNS (
Scope.accept_ptr_result): the name must be in scope, and the forward resolve must land back in the same /24 the reverse lookup came from. An unconfirmed PTR record alone proves nothing. - vhost probing in deep mode also skips shared-infra IPs, and only counts a candidate if its response fingerprint differs from a baseline probe using a nonsense Host header on the same IP.
sources (passive, no key) ┐ sources (active: brute, AXFR) ├→ candidates → resolver (wildcard-aware) dns_extra (SPF/DMARC/SRV) ┘ │ ▼ permutation round (dnsgen-style) │ ▼ (deep mode only) TLS SAN · HTTP probe + crawl · PTR sweep (FCrDNS) · vhost │ ▼ SQLite (history/diff) + JSON/CSV/TXT export subscout/core/: models, scope/anti-noise rules, resolver, permutations, DNS record parsing, the pipeline orchestrator.subscout/sources/: pluggable passive-collection sources.subscout/enrich/: deep-mode correlation: ASN, TLS, HTTP, crawl, PTR, vhost, port scan, buckets, NS/NSEC, GitHub code search.subscout/storage/: SQLite history/diff store plus JSON/CSV/TXT export.subscout/runner.py: shared scan-execution and result-printing logic, used by both the CLI and the console.subscout/cli.py: one-shot, flag-driven front end (Typer).subscout/console.py: the persistent, msfconsole-style console.subscout/banner.py: the startup banner.
- Tor/bridge support is planned but not implemented yet.
- API-key sources (VirusTotal, SecurityTrails, Shodan, Censys) aren't wired in yet.
- The dependency-free core logic (
core/models.py,core/scope.py,core/permutations.py,core/dns_extra.py,storage/) was written and tested directly. The resolver/pipeline tests that needaiodns/httpxare written with mocks (tests/test_resolver.py,tests/test_pipeline.py) but have only been syntax-checked (py_compile), not actually run. Before relying on this tool, runpip install -r requirements.txt && pyteston a machine with normal internet access, and do a test scan against a domain you control to confirm wildcard filtering and PTR gating behave as expected.
Only run this against domains you are authorized to test. AXFR attempts, brute force, and vhost probing all touch the target's infrastructure directly.